
Claude Found a Xen VM-Escape Flaw
Xen disclosed two grant-copy flaws on November 3 that let a malicious VM read and write the memory of any VM on the same host, even privileged domain Dom0. The advisory credits Claude with finding them; all versions 4.6 and above are affected, and only a patch plus reboot fixes it.
- 01THE DISCOVERY — Claude discovers; Ada Logics verifies.
- 02THE DISCLOSURE — Security advisory XSA-523 published on November 3.
- 03THE PATCH — Upstream patches cover up to Xen 4.17.x.
WHAT HAPPENEDWhat Happened
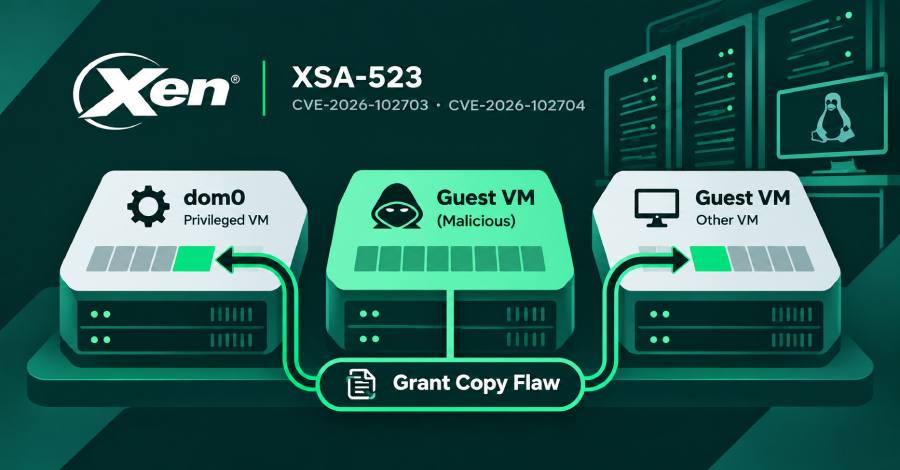
Xen published security advisory XSA-523 on November 3, disclosing two grant-copy flaws, CVE-2026-102703 and CVE-2026-102704. A malicious VM can read and write the memory of any VM on the same host, even privileged domain Dom0: a complete VM escape.
The advisory's acknowledgments credit Anthropic's Claude with discovering the flaws, verified by Stephan Lipp of Ada Logics, with the CodeAnt AI security research team reporting them independently afterward.
All Xen versions 4.6 and above are affected; 4.5 and earlier are not. The advisory states there is no known mitigation; the only fix is to patch and reboot the host.
WHAT WENT WRONG IN GRANT COPYWhat Went Wrong in Grant Copy
CVE-2026-102703 confuses frame numbers with grant references in cached grant-copy state. CVE-2026-102704 places the check that restricts per-frame copying to a VM's own memory in the wrong place.
Both are small mistakes with large consequences. One misplaced check breaks isolation in one place, and the wall between VMs is left paper-thin.
WHY NO MITIGATIONWhy No Mitigation Exists
The advisory's own words: there is no known mitigation. No configuration workaround exists; only patching, and the patch takes effect only after a host reboot.
Upstream patches cover only up to Xen 4.17.x. Versions 4.6 to 4.16 have no patch in the advisory; security support for 4.16 ended on December 2, 2024.
A NEW DIVISION OF LABORA New Division of Labor in Finding Flaws
A model is named as discoverer in a security advisory's acknowledgments for the first time. Discovery, verification, and independent reporting took two people plus one model.
Flaw-finding is now outrunning patching. Discovery can be automated; fixing and rebooting still take human hands, and the gap sits in the last mile.
THE SHIFTWhat Changed
SIGNAL JUDGMENT — ANALYSISModels Now Find Flaws Faster Than Patches Ship
Tokenta Signal's judgment: the real lead in this Xen advisory is the byline. A model is named as discoverer in a security advisory for the first time, and the craft of auditing is changing hands.
WHAT REMAINS UNCERTAINWhat Remains Uncertain
EVIDENCEEvidence
Xen security advisory XSA-523 confirms two grant-copy flaws, CVE-2026-102703 and CVE-2026-102704, found by Anthropic's Claude, letting a malicious VM read and write the memory of any VM, even Dom0, with all versions 4.6 and above affected.
PRIMARY SOURCESPrimary Sources
- Xen security advisory: XSA-523: arbitrary read/write via grant copy
https://xenbits.xen.org/xsa/advisory-523.html - The Hacker News: Xen Hypervisor Flaws Let One Malicious VM Read and Write Any Other VM's Memory
https://thehackernews.com/2026/11/xen-hypervisor-flaws-let-one-malicious.html
RELATEDRelated Intelligence
- Microsoft Winds Down Its Oracle AI Cloud Rental as Older Nvidia Chips Fall Behind
- An Unreleased Anthropic Model Proved an 18-Year-Old Quantum Conjecture, Machine-Checked in Lean
- IBM Unveils Quantum System Two in Chicago, Its Most Advanced Computer Yet, Powered by Nighthawk
- Vistra Posts $1.14B Q3 Profit as Power EBITDA Jumps Over 50%, Lifts 2026 Outlook